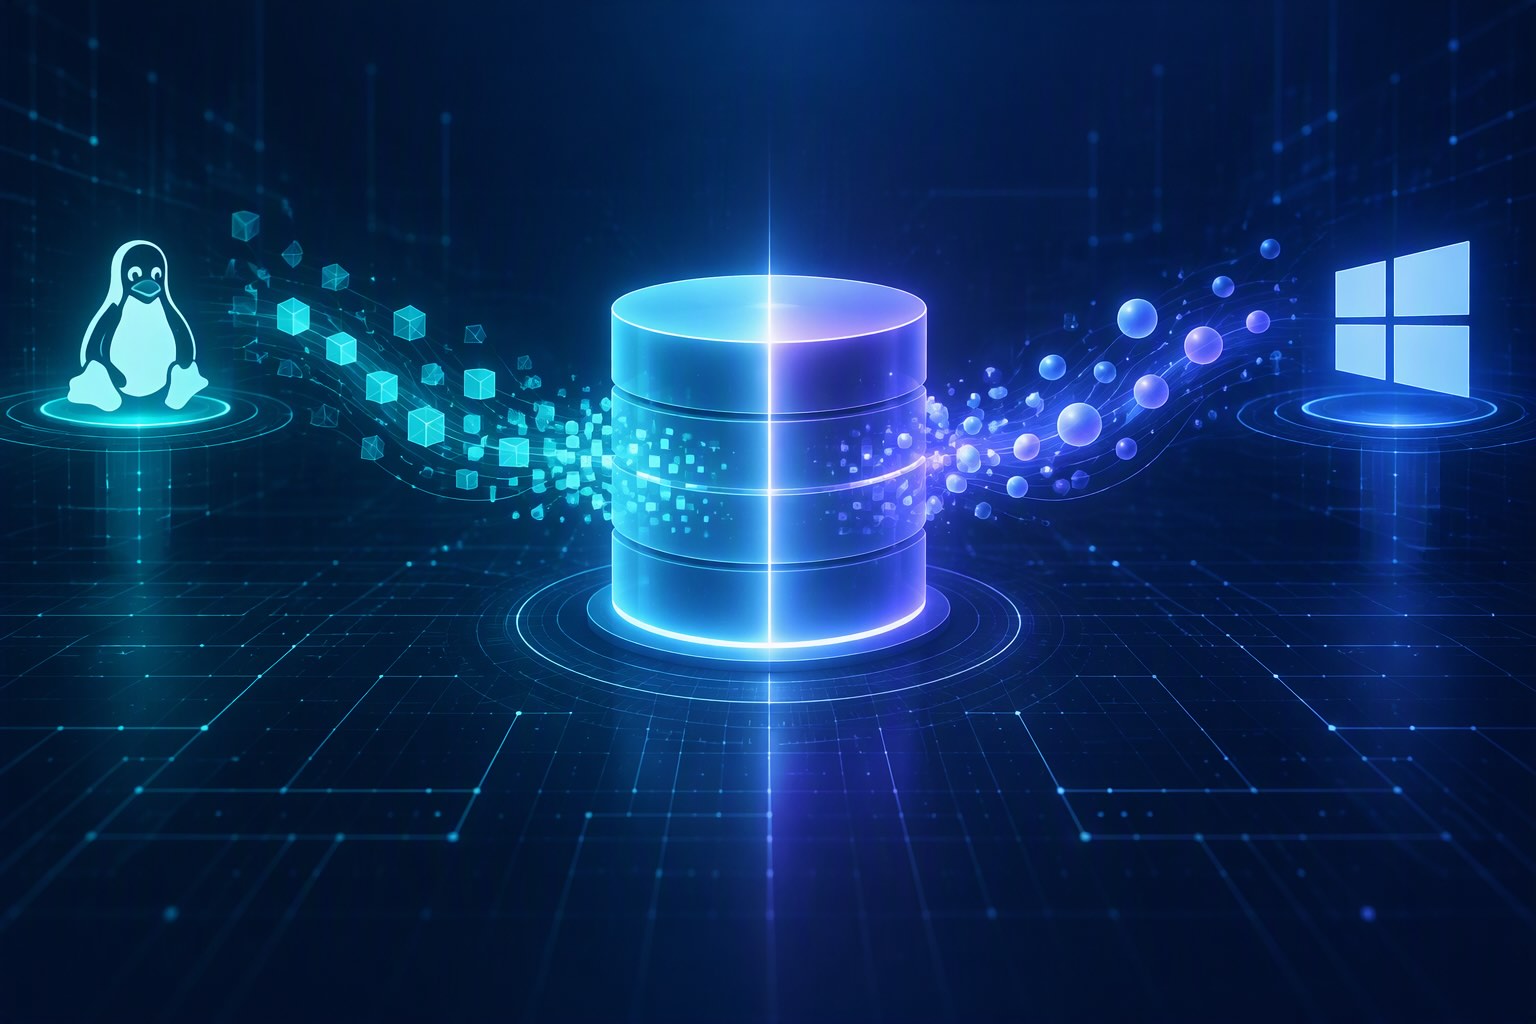
Dual-protocol volumes in Azure NetApp Files are one of those features that sound like a solved problem in the Azure portal and turn into a support ticket in production. The pitch is simple: one volume, mounted over NFS from your Linux estate and over SMB from your Windows estate, same files, same byte stream underneath. The reality is that NFS and SMB were built around two genuinely different permission models, and a dual-protocol volume doesn’t dissolve that difference — it just forces you to pick, upfront, which model wins when they disagree.
Most of the pain reports that show up in forums and support threads trace back to one decision made too casually at volume-creation time: the security style. Get that one choice right, understand what it actually does under the hood, and the rest of dual-protocol design is straightforward. Get it wrong, or treat it as a default you don’t need to think about, and you’ll be debugging “permission denied” errors from the wrong side of the protocol divide months later.
What a dual-protocol volume actually is
Azure NetApp Files volumes come in three flavors: NFS-only (NFSv3 or NFSv4.1), SMB-only, or dual-protocol — NFSv3 and SMB together, or NFSv4.1 and SMB together, on the same volume. The appeal is obvious anywhere you have mixed Linux and Windows clients that need to see the same dataset: a shared research data set, a media repository, a home-directory volume serving both platforms, or a Kubernetes cluster with both Linux and Windows worker nodes that need the same persistent volume exposed over NFS to one and SMB to the other.
Underneath, though, SMB and NFS carry fundamentally different identity and permission models. SMB authenticates against Active Directory and expresses permissions as NTFS ACLs tied to Windows SIDs. NFS — especially NFSv3 — authenticates by UID/GID and expresses permissions as POSIX mode bits (owner/group/everyone, read/write/execute). A dual-protocol volume has to reconcile a Windows SID-based permission check with a UNIX UID-based one on literally every file access, regardless of which protocol the request arrived on. That reconciliation is called name mapping, and it’s the mechanism the rest of this post is really about.
The core decision: security style
Every dual-protocol volume has exactly one active permission model at a time, called its security style, chosen at volume creation: NTFS or UNIX. This single setting determines which protocol “owns” permission semantics for that volume, and it cannot do both at once — a dual-protocol NAS environment only has one active permission style, period.
- NTFS security style: permissions are stored and enforced as Windows NTFS ACLs. Windows clients manage permissions normally through the Windows permission model. NFS clients can read and write files, but they cannot change permissions —
chmodandchownfrom an NFS client have no effect on an NTFS-security-style volume. Every NFS access requires a UNIX-to-Windows name mapping before the server can evaluate the NTFS ACL against it. - UNIX security style: permissions are stored as POSIX mode bits, or optionally NFSv4.x ACLs (not POSIX ACLs — Azure NetApp Files doesn’t support those). NFS clients manage permissions the way they always have. Windows clients can read and write, but can’t manage permissions through the Windows ACL editor the way they’re used to — the Windows ACLs extended attribute set/get isn’t supported from the SMB side, so Windows clients can’t change permissions for UNIX-style dual-protocol volumes either.
Put simply: whichever side didn’t get picked as the security style loses its native permission-management workflow. This is the fact that gets lost in dual-protocol’s “just works for both” marketing, and it’s the single most important design decision in this entire feature. The right question to ask before creating the volume isn’t “do we need both protocols” — you already know that — it’s “which side needs to actually manage permissions, day to day, through tooling its admins already use?” Pick NTFS if your Windows admins need to keep setting granular ACLs through familiar tooling and your Linux workload is mostly reading and writing data without touching permissions. Pick UNIX if the reverse is true.
Pitfall 1: the mismatched-security-style “permission denied”
This is the single most common dual-protocol support thread, and it has a specific, recognizable shape: an NFSv3 client hits an NTFS-security-style volume and gets denied — even as root. The underlying cause is almost always a broken or missing name mapping: the NFS client’s UID doesn’t resolve to a Windows identity that holds permission on the NTFS ACL, so there’s nothing for the server to grant access against. No identity, no decision, default deny.
Concretely, troubleshooting this means checking, in order:
- Is there an LDAP (or equivalent) directory configured that Azure NetApp Files can query for UID-to-username resolution?
- Does the UID presented by the NFS client actually correspond to a real AD user with a populated
uidNumber/gidNumber? - Does that resolved Windows identity actually hold the permission being requested on the NTFS ACL?
Miss any one of the three and the access attempt fails, frequently in a way that looks like an ACL problem when it’s actually an identity-resolution problem one layer upstream. If no valid UNIX username exists for a Windows user trying to access a UNIX-security-style volume, there’s a defined fallback — a default UNIX user, pcuser, numeric UID 65534 — but there’s no equivalent fallback running the other direction. An NFS client with no resolvable Windows identity on an NTFS volume simply fails; the absence of a default-deny-to-somewhere behavior there is a deliberate asymmetry worth knowing about rather than discovering live.
Pitfall 2: assuming NFSv4.x ACLs behave like POSIX ACLs
If you’re on UNIX security style and reach for NFSv4.x ACLs instead of plain mode bits — a reasonable move, since NFSv4.x ACLs offer much more granular control, closer to what Windows admins expect from NTFS — know that they are not POSIX ACLs, and the platform doesn’t support POSIX ACLs at all. NFSv4.x ACLs can be applied from any NFSv4.x-capable administrative client and will be honored even by NFSv3 clients mounting the same volume, which is genuinely useful. But they interact with SMB access the same way mode bits do: Windows usernames still need to map cleanly to UNIX usernames for the permission check to resolve, and the same pcuser fallback applies when that mapping is missing.
The practical trap here is building an access model entirely around NFSv4.x ACL semantics and assuming it translates one-to-one with what a Windows admin sees in an NTFS ACL editor — it doesn’t, because the volume is still UNIX security style underneath, and the SMB side is along for the ride rather than a first-class citizen of that permission model.
Pitfall 3: treating the protocol-version choice as cosmetic
A second axis of decision sits underneath the security-style choice: NFSv3 versus NFSv4.1 as the NFS half of the pair. This looks like a minor version bump; it isn’t. NFSv4.1 brings integrated locking, a stronger ACL model, and — for specific workloads — is a hard functional requirement rather than a preference. SAP HANA is the clearest example: NFSv3 is explicitly unsupported for the /hana/data and /hana/log volumes, and NFSv4.1 is mandatory there for functional reasons, not just as a best practice. Apache ActiveMQ is a documented example on the opposite end — file locking behavior makes NFSv4.1 the recommended choice even though NFSv3 would technically mount and serve files without complaint.
The design implication: validate the actual application’s NFS version requirement before the volume is created, not after. Azure NetApp Files does support converting a volume between NFSv3 and NFSv4.1 after the fact without a data copy, but the conversion requires an application downtime window while clients unmount, the export policy switches, and clients remount with the new protocol version in their mount options — and converting down from NFSv4.1 to NFSv3 means losing NFSv4.1 features like ACLs and file locking entirely, not just suspending them. Also worth flagging directly: NFSv4.2 isn’t supported at all, and NFS clients that negotiate their highest available version automatically can silently end up speaking NFSv4.2 against what’s actually an NFSv4.1 server — this is a real, documented source of mount hangs and timeouts, and the fix is to explicitly pin vers=4.1 (or nfsvers=4.1) in client mount options rather than trusting auto-negotiation.
Pitfall 4: forgetting LDAP is now load-bearing infrastructure
Every pitfall above routes through the same dependency: name mapping requires a working LDAP connection back to Active Directory (or another supported directory) with UID/GID POSIX attributes populated on user objects. This is easy to treat as a one-time setup checkbox during volume creation and then forget about — until an access-denied report comes in and the actual root cause is a user object that was created without uidNumber/gidNumber populated, or an LDAP search scope that doesn’t cover the OU the user lives in.
Two details worth building into the design rather than discovering during an incident:
- A reverse lookup zone with a PTR record for the AD host is a creation-time prerequisite for dual-protocol volumes — its absence fails the volume creation outright, not just LDAP lookups later.
- For larger AD topologies using UNIX security style with LDAP and extended groups, the LDAP Search Scope setting on the Active Directory Connections page needs to be configured deliberately; the default scope is a documented source of “access denied” errors on Linux clients specifically, in large directory topologies, that have nothing to do with the files’ actual permissions.
If your organization’s process for provisioning new AD users doesn’t reliably populate POSIX attributes — a common gap, since plenty of AD environments were never built with NFS in mind — that gap becomes a dual-protocol access problem the day someone new needs to touch the volume from Linux.
Design choices, summarized
| Decision | Options | What it actually determines |
|---|---|---|
| Security style | NTFS or UNIX | Which protocol’s clients can natively manage permissions; the other protocol gets read/write access but not permission management |
| NFS version | NFSv3 or NFSv4.1 | Locking model, ACL capability, and whether specific applications (SAP HANA, ActiveMQ) will even function correctly |
| ACL model (UNIX style only) | POSIX mode bits or NFSv4.x ACLs | Granularity of permission control available from the NFS side; NFSv4.x ACLs are honored by NFSv3 clients too, but aren’t equivalent to NTFS ACLs from the SMB side |
| Name-mapping source | AD LDAP, with POSIX attributes populated | Whether access attempts resolve to a real identity at all, independent of whatever the ACL says |
| Chown mode | Restricted (default) or Unrestricted | Whether non-root NFS users can transfer ownership of files they own — a quieter but real security-posture decision alongside the security-style one |
A practical recommendation
Start by identifying, honestly, which side of the protocol divide will actually be setting permissions on a day-to-day basis — not which side will technically have clients mounted, but which admins or automated processes will be running chmod/chown or editing NTFS ACLs. That answer picks your security style; don’t let it default to NTFS just because that’s the portal’s default selection.
Validate the NFS version against your actual application’s documented requirements before volume creation — treat “does this app have a stated NFS version dependency” as a mandatory design question, the same way you’d check a database’s supported OS versions, rather than letting it default to whatever the team creating the volume happened to pick. Converting later is possible but costs you a maintenance window and, if you’re downgrading from 4.1, a real loss of functionality.
Treat the AD/LDAP connection and its POSIX attribute population as part of the dual-protocol volume’s design, not a prerequisite you check off once and forget. If your organization’s AD provisioning process doesn’t already populate uidNumber/gidNumber on new users as a matter of course, fix that process before the volume goes live — not after the first access-denied ticket arrives from someone who was provisioned normally for Windows and has never touched Linux-side identity before.
The platform engineering takeaway
Dual-protocol volumes solve a genuine problem — mixed-OS environments that need one shared data path instead of two parallel copies kept awkwardly in sync — but the feature’s apparent simplicity in the portal hides a real architectural decision that most other storage choices don’t force on you: picking a side in a permission model conflict that NFS and SMB were never designed to agree on. Treat the security-style and protocol-version choices with the same weight you’d give an irreversible infrastructure decision, because functionally, several parts of this one are: changing security style after the fact isn’t a documented, supported operation the way NFS-version conversion is, and getting it wrong early means rebuilding the volume rather than just filing a bug.
Discover more from ksharp
Subscribe to get the latest posts sent to your email.